Friday, June 5, 2020

Top 10 Best Google Gravity Tricks 2018

Best Google Gravity Tricks 2018

Top 10 Best Google Gravity Tricks 2018

Google is the search engine where the people look up for the things. Yet apart from being only a search engine this website is highly functional and has a lot of functions dubbed inside it. And even the webmasters don't know about all the features as they are so vast that you need to explore lots of things to get to know about them all.  There are a number of gravity opposing tricks in the Google search page that you would like to enjoy. Well many of you guys must be new to this word as only 15% of Google users know this thing and for rest, I'm here to guide you up in this. Here in this article, we have written about the best google gravity tricks that you could ever find in this year. If you are interested to know about it then please read the main section of this post as it is given below. This was all the introduction part of this post and now after this line, we are going to skip to the main section. We recommend you to read till the end to get the fullest information from this page!

Top 10 Best Google Gravity Tricks 2018

Below I have mentioned some of the best tricks that I tried as I was getting bored and thought about exploring something new and then I searched Google Tricks on google and then I get to know that even these things are also possible on the Google. You can use so many different things to kill your boredom on Google. There I decided to note down these tricks and share the article with you so that you can also avail these. So follow the below guide to proceed.

#1 Google zero gravity level fall
Best Google Gravity Tricks 2018
This is the first trick that amazed me as when I get to know this thing can happen when I was really surprised as it was quite funny. It is a standout amongst the most astonishing google gravity trap. In this trap, the substance will appear like tumbling to a level surface. Every one of the substances like pictures, writings, and so on of your page will be upset. They will look somewhat bouncy and turned around that looks exceptionally energizing and stunning.

#2 Google Sphere
Best Google Gravity Tricks That You Need To Try
This is second best google gravity trap. In this trap, the substance rotates in a round way. Be that as it may, you will think that its little hard to deal with it since you need to chip away at turning writings.

#3 Google Loco
Best Google Gravity Tricks That You Need To Try
This google gravity trap is much like the google zero gravity. You will see the substance as falling in a seismic tremor,

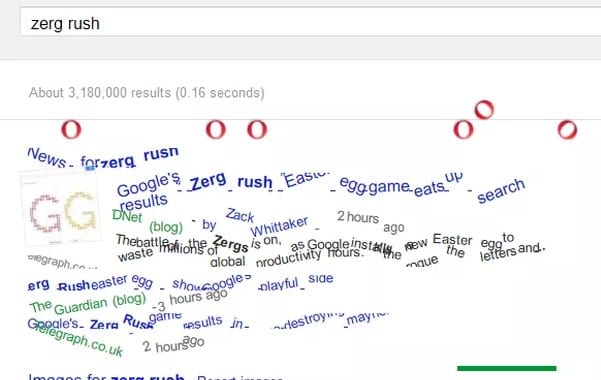
#4 Zerg Rush
Best Google Gravity Tricks That You Need To Try
This is one of my most loved google gravity trap. In this deceive you will see somewhere in the range of zeros spreading in your page. to utilize this trap Open Google.com and hunt Zerg Rush through utilizing the search bar.

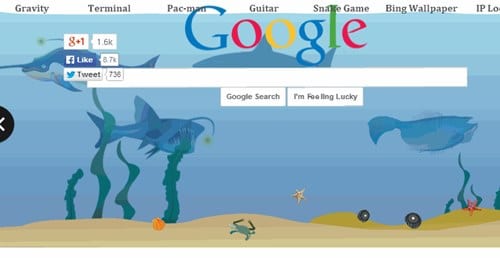
#5 Google submerged
Best Google Gravity Tricks 2018
This is of the most attractive google gravity trap. In this deceive you will see a domain of submerged. You will see the pursuit bar coasting in the water.

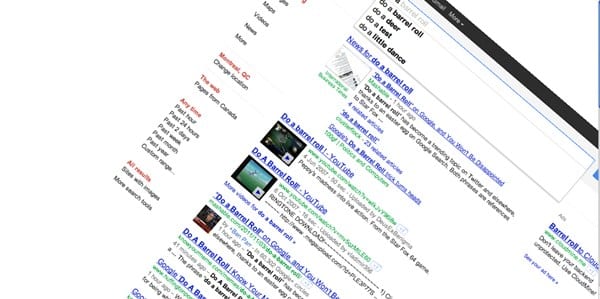
#6 Do a barrel roll
Best Google Gravity Tricks That You Need To Try
This is likewise an astounding google gravity trap. In this deceive, you will get an impact to your page with which, your page will turn in a solitary minute.

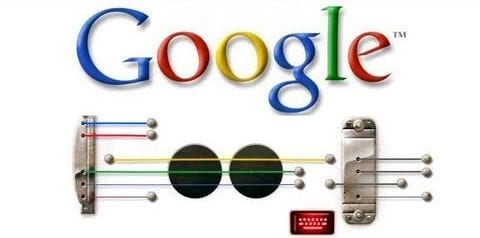
#7 Google Guitar
Best Google Gravity Tricks That You Need To Try
This is additionally a stunning google gravity trap. In this deceive, you can play guitar on the web index. You can play your coveted tunes with it. Google will give you notes to your tunes.

#8 Google zero gravity reversal
Best Google Gravity Tricks 2018
This is one of the coolest Google gravity trap. In this deceive, you will get a perfect representation of your site page. You will feel like you are on the opposite side of the screen.

#9 Google space
Best Google Gravity Tricks That You Need To Try
In this google gravity deceive you encounter a dream of the room. It implies that the substance of your page will appear like gliding noticeable all around with no gravitational power.

#10 Pacman
Best Google Gravity Tricks That You Need To Try
Best Google Gravity Tricks 2018 That You Need To Try
This is the standout amongst the most energizing google gravity trap. With this deceive, you can play Pacman game in this.
Finally, after reading this article, you have got to know about. We have tried to provide you this content in the simple and easy to read wordings and hope that you would have easily got about everything written up here. We believe that you might like this article and if it is what you think then please try to share it with others too. Your indulgence in our post is really valuable to us, so do not miss to write about your opinions and suggestions regarding this article through using the comments section below. At last but never the least thanks for reading this article!
Related word

Masad Clipper And Stealer - Windows Spyware Exfiltrating Data Via Telegram (Samples)


Reference


"Masad Clipper and Stealer" steals browser information, computer files,  and automatically replaces cryptocurrency wallets from the clipboard with its own.
It is written using Autoit scripts and then compiled into a Windows executable.
It uses Telegram to exfiltrate stolen information.


Download

             Other malware


Hashes

SHA256SHA1MD5
1acf5a461ee16336eb8bbf8d29982c7e26d5e11827c58ca01adac671a28b52ad6001b34c17c122d201613fffd846b056614b66dae03234c2259c474aeb69500423ddeed7
290a1b89517dec10bfd9938a0e86ae8c53b0c78ed7c60dc99e4f8e5837f4f24a32800c10588053813f55bf8c87771311c5f7f38e2df4c1cf093c8373a8f2f194e77b69a2
7937a1068f130a90b44781eea3351ba8a2776d0fede9699ba8b32f3198de045ba2a67b06344e4f1cf85086f6b584316ec53d5e548368f1c4d8f0d908f5f4ff671df5f1da
87e44bca3cc360c64cc7449ec1dc26b7d1708441d471bf3d36cd330db35762942fe5483e6b82220eeeef12e531eb3347fea16ac11082ce517dd23eee335bedfc6bcd8205
cf97d52551a96dacb089ac41463d21cab2b004ba8c38ffc6cb5fb0958ddd34db5b79a15cb61f5260f0b9d807faa160e6d49590e4b5fdf9653eb1ffbdae8cb4f1f2d71747
79aa23c5a25c7cdbaba9c6c655c918dac3d9823ac62ebed9d7d3e94e1eaafc074a279a6b82fe801d3c8be9d16df2ef5623b177040029ab0fd56cd7e493b46a331ef18bd3
03d703f6d341be258ac3d95961ff0a67d4bf792f9e896530e193b091dca29c2ea9740352af2c9cc926deba7dffc452f213f7f05fa462aac76def5b53351b3b1ddb41124c
a368b6755e62e5c0ff79ea1e3bd146ee8a349af309b4acf0558a9c667e78293ae16167ab646381c277c2ca84319ceb57bacb2c92c4cdc7665adb1cda5897d4df4a560f88
ba933cefbe9a8034f0ba34e7d18481a7db7451c8ef4b6172fb0cad6db0513a5100749407e97085af470c75ef004f2235d30af44fc26a3f2317507a09d91014469b045384
3ba3c528d11d1df62a969a282e9e54534fb3845962672ad6d8bbc29cb6d062f5b8100890c0f1894544b3f99168377ec46c38e9114a0607b4488cd539b8b0b443abd121e3
b763054180cd4e24c0a78b49055ad36dbc849f1a096cddf2db8cee0b9338c21d7bec99308ce4bf409417b642cd9432000a5c19d22dfb1d606e5539399aa1a536baafd2f8
d5ce4b04b7eec6530a4a9d40510177468fadc235253e5a74530a8c9d990f3c5027fc204ffa42262b7570b6fccb435d4d38a3610fc5d8b73da810646407c333fe52186281
965a5949d8f94e17ebcd4cb6d0a7c19f49facbfc1b1c74111e5ceb83550d6c8f7698584b2e7c62061447a6a2583ed6957180c205e7ebe4411664672359b393f530fc2fc1
44134b9d4b10d94f6381b446a1728b116d62e65c1a52db45235af12caf7e38c0fd114077927d501606575ba9ab38ecfb3407d432a4388980d7e3539d74a950dab23d00ac
848d76a227f4fe282b7ddfd82a6dfc4c25da2735a684462b42fe4e1c413d8e34135cee7610890497183eb6251efef307ea013fe17bb23077b4f80df48b91b425eda05828
5ca0a957fe6c253827f344da4ba8692d77a4e21a1df4251594be2d27d87dd8aed231874332ca462fb462e4f68450d2c2c22d4bcddda77b3f3f74a2bdffd167917686e139
016fa511f6546ed439d2606c6db8821685a99f5a14ef3f710668b58dc89c69265c83749c62ee0131710bf26931cb1e463a8fbda3b0c34df85677d8f752dc1e1a5eeba0c9
22be594fbfa878f631c0632f6c4d260b00918817ff66a1f9f15efe44c1a58460856d635fca52631305f1fefc58eafa74496524b660ebf41953d5c6e212fc306cdb0c6519
f3571ec66288405dab43332ca03812617f85fb08832fbbe1f1d89901fe034b8a819485e20d841195e2e8a7ae5b41ff709887bb216984d37863c08b9fdd969297d35d3538
04c949eca23103b1de05278b49f42c3ab6b06f4bf20aafa5f2faefaa84c16ecd0487db2df1802dd4ee4ae3b62b5f08937dd5c77c4366ee61cbd7e636aea8540836a60036
d6fc04acda8f33a6d35eb577c27754c2f2b4d6f4869576c7c4e11b2c5e9b017683ae89826114662dad8553d5eeed5217b57047f22bc964e294d7ab314c34e5934d91a5a9
18c0bd4dd98008383fc52045ad896449fa7f0037593bb730ed1ef88aa547006dbcaa05b60a9d625852ac4f2d0d805ab16498815535d9f08c39c4cf396427f3a345e5c09a
4c9d5469e9095813418260045c2b11e499e4eaa0ffb25293f90f580c464157df4c6aacc0b893ed366f9f307326e59efa61e5153450dddaf7e5bb24aabf66eecd0c8b79cf
0b5f1fbc05dc8baca492b748adeb01fb4904e02723b59211ecde222f7b12d91e87f898e0d41c0f2c22d4e9278a942326877fc368da780b72140535d4c2d391e76dc8181d
31ad5c4547ceae4d0550c8460524c16a6105afc056760e872c4966656256c9dc37f485d3fa8f6cf13061cb1ea38ae0d5d2edfd95134aefcf640c24a1ab5344a96150fb05
edb00a0e5ff70e899857549e3263c887a799416c8bbab43ab130ca1be9bbd78c42c30dc551a3cb3bc935c0eae79b79f17942e439c2722241f765d2ad4fb58edd76a4adea
96f852b81760a425befaa11ea37c0cdea2622630bf2a0c94bb95042211ab614d5d9782064bc38d40c88f32c0410479cbd61caa40f332cfcda8c0ef579ede59eff23caa1e
57fd171a5b1a88e9583b42439851a91a940eb31105ab29cb314846da2ed43b820bfec2059823b936d782bea7bc16abd9923dddb56fff82df7a565b4570d299486697310f
277018b2cc6226dca6c7678cac6718c8584f7231340ad8cd7c03477559fdf48b261f916ce97ffc6817a4772705df68e6ccca8181009dc7d8766a85d85bb6a26ee69b66fe
e968affb1fc7756deb0e29807a06681d09a0425990be76b31816795875469e3dcf78484a999183324da9affdf2aaeff508d1dc473e1b8f6313447b8a4b49671ddeb8a4ee
4b1ccf6b823ee82e400ba25b1f532cd369d7e536475a470e2011b77ffeaf7bb3bc988f7cd32d411f2a9888afc72c7a892e2a1def55128a3da6f70129acdbf9dbe955cfe7
fc84d6636a34ad1a11dbaa1daec179e426bdcd9887b3d26dc06b202417c08f951df31bec02e35c9a4656bb3a3bdf631bb37605a855d77ab16377a8a314982f723fcc6fae
9ca15f15fbae58cb97b0d48a0248461e78e34e6d530338e3e5b91f209a1662678505dfaad6d10b84c73544eb748d547cb5bad9bdebc12c530dab0a65c37ffd72612fa705
31f3a402c1662ed6adffbf2b1b65cf902d1df763698eb76d21e4e94b4c62971418c972722d984ff6da2bc26a0aca4c7f209cc39c05bbf6e72b5b24c0c81e0671bf17b1e7
8d9f124ddd69c257189f1e814bb9e3731c00926fc2371e6ebe2654f3950ca02e553cd98c83e945ee3013aa40897baec0305b34a2b4030025e039c54c2d3923057447494c
a0923d7645604faaa864a079adeb741a5d6e65507a2819b2fee4835d396077d9f8e6995e28c789d8b24e982ac53d5d6ba453de73b796f85c8a7de71407d6e3c4206edda3
a19b790ea12f785256510dde367d3313b5267536a58ca0c27dbdac7c693f57e1a92f7393daf7ead9a44b12e35f850705798fc879a6defec886d31f6375712466dd794a96
f030fb4e859ee6a97c50c973a73dced3640befe37f579cfd15367ce6a9bbede2ad3a1e779f02539ccd07bff735e0823add9730b2c259564a8fe72333604a5686e30f6242
f01db6d77ac21211992ceae4e66e1e03c1cb39d61e03645b9369f28252ca769314c6bf63ff4d32d8a0a42e81ea39304fb7ab13c880fe593ef5538fbf66b3b3e1cb7b9b8b
dfe3d0e95feaed685a784aed14d087b019ba2eb0274947a840d2bdbae4ae36742107d057478328df8f538102508de00b0c4b37c7b5a85a0e7a2c4197c3794c8bb2eb5763
bf6083040ca51e83415f27c9412d9e3d700bd0841493b207bc96abf944ab0ca709a695ce6c35c029dd7577e29f403d7144698b417a2edceb31a9c0d05e5f13c6caee0576
b154151dc8ace5c57f109e6bb211a019db20c4f0127c4d13c7703f730bf492768c0cda049c85493df4e97db3db4ddc94075ba62cb6a895ac5ba5b6472680d47410a238a5
6bf6b1bde63cee9b81902efd187fdd56ecee5853754ce0a19d5ab5c3b02429886e2d4f0bcc97ce130ae89647f648d3e96548a391a29f9d176b913e7f693355700aaadbb9
0dcf547bd8f4074af97416d8b84ea64b2f3319064aa4bce64ad0c2e2d3957175a996b925e9391a69140caf6e4adba928694ffe66dd575413a40839f2807593aa21c71152
6cff1249cc45b61ce8d28d87f8edc6616447e38168e610bed142f0b9c46ea6849baa823deb9075e8df77b891115c019244de09de488bb5c0739485721182c01a82b01d14
5b5ebe019806885bbaafe37bc10ca09549e41c240b793fd29a70690a5d80b4963d46711f9064b96ff2d0affdef1ecd82d120659db95e2d8a8509ac05f5445d18d32cc7cb
103d87098c9702cab7454b52869aeeb6a22919f29a7f19be7509255ce2d8c83ee29a163488438c9ea9014ddf1a9b2d382cc5d7e6baf2587fafaedbab4a78b9b7fd8b55f8
c73675005a09008bc91d6bc3b5ad59a630ab4670dca6ac0d926165a3ecfd8d92d8ea2280cd06a5cc32b7d668e2b4b2e68f3a7e2a98ecc6fbb2cb5649daf751fcbfb81bcb
ef623aadd50330342dc464a31b843b3d8b5767d62a62f5e515ac2b380b208fbe620ff5a7aaf7f3fcf4abc9365e0e77b3ec4b434db14535c5835c9dfb3cbbc7f6fef6034c
More info

  1. Pentest Hardware
  2. Hacking Groups
  3. Hacking Bluetooth
  4. Hacker Prank
  5. Hackerx
  6. Hacking Vpn
  7. Hacker Anonymous
  8. Hacking Lab
  9. Pentest Tools Free
  10. Hacking Names
  11. Hacking With Raspberry Pi
  12. Hacker0Ne
  13. Hacking Names
  14. Pentestmonkey Sql Injection

Thursday, June 4, 2020

How To Remove Write Protection From USB Drives And Memory Cards

If you've got a USB drive or SD card that can't be formatted and to which you can't copy files, then take a look at our guide to removing write protection.

Sometimes you'll find that it's impossible to format, delete or copy new files to an SD card or USB flash drive. Windows will tell you that it is write protected, even though there is no 'lock' switch or – if there is – you've made sure the switch is set correctly to allow files to be written to the drive.
But just in case this switch is news to you, it is well worth checking that your device has the switch set to 'unlocked'. When set to 'locked' you won't be able to copy any new files on to the memory card or USB stick, and it also stops you from accidentally formatting it.
iemhacker-remove-write-protection-from-usb
You'll still be able to view files which are already stored on the drive, but you can't delete them (they sometimes seem to delete OK, but the next time you check, there they are again!).
ut if this isn't the problem, you might still be able to fix things and continue to use your USB flash drive or SD card – we'll explain how.
Unfortunately, in some cases the device may be corrupt or physically broken and no tricks or software will make it work again. The only solution in this case is to buy a new drive. And if you're just trying to get back lost data, see our guide on How to recover deleted filed for free.
iemhacker
In any version of Windows from XP onwards, run Regedit.exe.
If you're not sure how to find it, searching 'regedit' in the Start menu will usually show the program at the top of the list.
It's a bit like File Explorer, so use the pane on the left to navigate to the following key:
Computer\HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\StorageDevicePolicies
Note: if you can't find StorageDevicePolicies, see the next step.
Double-click on the WriteProtect value in the right-hand pane. You can now change the Value data from 1 to 0. Then click OK to save the change. Close Regedit and restart your computer. Connect your USB drive again and, with a bit of luck, you should find it is no longer write protected.
You can now continue to use the drive, but it's worth copying off any files you want to keep and then formatting it by right-clicking on it in the list of drives in File Explorer and choosing Format.

StorageDevicePolicies

If you can't find StorageDevicePolicies, you can create it by right-clicking in the white space in the 'Control' folder and choosing New -> Key and entering the name StorageDevicePolicies.
Now double-click on the new key (it will show as a folder) and right-click once again in the white space and choose New -> DWORD. Name this WriteProtect and set its value to 0. Click OK, exit Regedit and reboot your computer.
If this method doesn't work, go to the next step.

Diskpart

iemhacker
With your USB drive or memory card attached to your computer, launch a command prompt. You can do this by searching for cmd.exe or 'Command Prompt' in the Start menu.
Note: you may need to run cmd.exe with administrator privileges if you see an "access is denied" message. To do this, right-click on Command Prompt in the Start menu and choose 'Run as administrator' from the menu that appears.
If you have Windows 10, simply right-click on the Start button (bottom left of the screen) and choose Command Prompt (admin).
Now, at the prompt, type the following and press Enter after each command:
diskpart
list disk
select disk x (where x is the number of your non-working drive – use the capacity to work out which one it is)
attributes disk clear readonly
clean
create partition primary
format fs=fat32 (you can swap fat32 for ntfs if you only need to use the drive with Windows computers)
exit
That's it. Your drive should now work as normal in File Explorer. If it doesn't, it's bad news and there's nothing more to be done. Your stick or memory card is scrap and fit only for the bin. But the good news is that storage is cheap.

Related links


Wednesday, June 3, 2020

Advanced Penetration Testing • Hacking The World'S Most Secure Networks Free PDF

More articles


  1. Pentest With Metasploit
  2. Pentest+ Vs Oscp
  3. Pentest Example Report
  4. Hacking Apps
  5. Hacking Script
  6. Pentest Jobs
  7. Pentest Report
  8. Hacker Kevin Mitnick

Learning Web Pentesting With DVWA Part 6: File Inclusion

In this article we are going to go through File Inclusion Vulnerability. Wikipedia defines File Inclusion Vulnerability as: "A file inclusion vulnerability is a type of web vulnerability that is most commonly found to affect web applications that rely on a scripting run time. This issue is caused when an application builds a path to executable code using an attacker-controlled variable in a way that allows the attacker to control which file is executed at run time. A file include vulnerability is distinct from a generic directory traversal attack, in that directory traversal is a way of gaining unauthorized file system access, and a file inclusion vulnerability subverts how an application loads code for execution. Successful exploitation of a file inclusion vulnerability will result in remote code execution on the web server that runs the affected web application."
There are two types of File Inclusion Vulnerabilities, LFI (Local File Inclusion) and RFI (Remote File Inclusion). Offensive Security's Metasploit Unleashed guide describes LFI and RFI as:
"LFI vulnerabilities allow an attacker to read (and sometimes execute) files on the victim machine. This can be very dangerous because if the web server is misconfigured and running with high privileges, the attacker may gain access to sensitive information. If the attacker is able to place code on the web server through other means, then they may be able to execute arbitrary commands.
RFI vulnerabilities are easier to exploit but less common. Instead of accessing a file on the local machine, the attacker is able to execute code hosted on their own machine."
In simpler terms LFI allows us to use the web application's execution engine (say php) to execute local files on the web server and RFI allows us to execute remote files, within the context of the target web server, which can be hosted anywhere remotely (given they can be accessed from the network on which web server is running).
To follow along, click on the File Inclusion navigation link of DVWA, you should see a page like this:
Lets start by doing an LFI attack on the web application.
Looking at the URL of the web application we can see a parameter named page which is used to load different php pages on the website.
http://localhost:9000/vulnerabilities/fi/?page=include.php
Since it is loading different pages we can guess that it is loading local pages from the server and executing them. Lets try to get the famous /etc/passwd file found on every linux, to do that we have to find a way to access it via our LFI. We will start with this:
../etc/passwd
entering the above payload in the page parameter of the URL:
http://localhost:9000/vulnerabilities/fi/?page=../etc/passwd
we get nothing back which means the page does not exist. Lets try to understand what we are trying to accomplish. We are asking for a file named passwd in a directory named etc which is one directory up from our current working directory. The etc directory lies at the root (/) of a linux file system. We tried to guess that we are in a directory (say www) which also lies at the root of the file system, that's why we tried to go up by one directory and then move to the etc directory which contains the passwd file. Our next guess will be that maybe we are two directories deeper, so we modify our payload to be like this:
../../etc/passwd
we get nothing back. We continue to modify our payload thinking we are one more directory deeper.
../../../etc/passwd
no luck again, lets try one more:
../../../../etc/passwd
nop nothing, we keep on going one directory deeper until we get seven directories deep and our payload becomes:
../../../../../../../etc/passwd
which returns the contents of passwd file as seen below:
This just means that we are currently working in a directory which is seven levels deep inside the root (/) directory. It also proves that our LFI is a success. We can also use php filters to get more and more information from the server. For example if we want to get the source code of the web server we can use php wrapper filter for that like this:
php://filter/convert.base64-encode/resource=index.php
We will get a base64 encoded string. Lets copy that base64 encoded string in a file and save it as index.php.b64 (name can be anything) and then decode it like this:
cat index.php.b64 | base64 -d > index.php
We will now be able to read the web application's source code. But you maybe thinking why didn't we simply try to get index.php file without using php filter. The reason is because if we try to get a php file with LFI, the php file will be executed by the php interpreter rather than displayed as a text file. As a workaround we first encode it as base64 which the interpreter won't interpret since it is not php and thus will display the text. Next we will try to get a shell. Before php version 5.2, allow_url_include setting was enabled by default however after version 5.2 it was disabled by default. Since the version of php on which our dvwa app is running on is 5.2+ we cannot use the older methods like input wrapper or RFI to get shell on dvwa unless we change the default settings (which I won't). We will use the file upload functionality to get shell. We will upload a reverse shell using the file upload functionality and then access that uploaded reverse shell via LFI.
Lets upload our reverse shell via File Upload functionality and then set up our netcat listener to listen for a connection coming from the server.
nc -lvnp 9999
Then using our LFI we will execute the uploaded reverse shell by accessing it using this url:
http://localhost:9000/vulnerabilities/fi/?page=../../hackable/uploads/revshell.php
Voila! We have a shell.
To learn more about File Upload Vulnerability and the reverse shell we have used here read Learning Web Pentesting With DVWA Part 5: Using File Upload to Get Shell. Attackers usually chain multiple vulnerabilities to get as much access as they can. This is a simple example of how multiple vulnerabilities (Unrestricted File Upload + LFI) can be used to scale up attacks. If you are interested in learning more about php wrappers then LFI CheetSheet is a good read and if you want to perform these attacks on the dvwa, then you'll have to enable allow_url_include setting by logging in to the dvwa server. That's it for today have fun.
Leave your questions and queries in the comments below.

References:

  1. FILE INCLUSION VULNERABILITIES: https://www.offensive-security.com/metasploit-unleashed/file-inclusion-vulnerabilities/
  2. php://: https://www.php.net/manual/en/wrappers.php.php
  3. LFI Cheat Sheet: https://highon.coffee/blog/lfi-cheat-sheet/
  4. File inclusion vulnerability: https://en.wikipedia.org/wiki/File_inclusion_vulnerability
  5. PHP 5.2.0 Release Announcement: https://www.php.net/releases/5_2_0.php


Related links
  1. Hacking Device
  2. Hacking Books
  3. Hacking Script
  4. Pentest Stages
  5. How To Pentest A Website With Kali
  6. Pentest Framework
  7. Hacker
  8. Hacking Jacket
  9. Pentest Ubuntu
  10. Pentest Cheat Sheet
  11. Pentest Wifi
  12. Is Hacking Illegal
  13. Pentest Hardware

ShodanEye: Collect Infomation About All Devices Connected To The Internet With Shodan


About ShodanEye
   This tool collects all information about all devices that are directly connected to the internet with the specified keywords that you enter. This way you get a complete overview.

   Here you can read the latest article about Shodan Eye: Shodan Eye Ethical Hacking Tool Release

   The types of devices that are indexed can vary enormously: from small desktops, refrigerators to nuclear power plants and everything in between. You can find everything using "your own" specified keywords. Examples can be found in a file that is attached:

   The information obtained with this tool can be applied in many areas, a small example:
  • Network security, keep an eye on all devices in your company or at home that are confronted with internet.
  • Vulnerabilities. And so much more.
   For additional data gathering, you can enter a Shodan API key when prompted. A Shodan API key can be found here

Shodan Eye Ethical Hacking Tool Release
   Before we start the year 2020, today there is a new big release ..! Please note, if you have already installed Shodan Eye on your computer, then it is worthwhile to read it carefully. Of course, even if you don't know this Shodan tool yet:
  • Shodan Eye goes from Python 2 to Python 3
  • Save the output of the Shodan Eye results
  • The entry of the Shodan password is no longer visible.

About Shodan Search Engine
   Shoan is a search engine that lets the user find specific types of computers (webcams, routers, servers, etc.) connected to the internet using a variety of filters. Some have also described it as a search engine of service banners, which are metadata that the server sends back to the client.

   What is the difference between Google or another search engine: The most fundamental difference is that Shodan Eye crawls on the internet, Google on the World Wide Web. However, the devices that support the World Wide Web are only a small part of what is actually connected to the Internet.

Before use this tool, you should note that:
  • This was written for educational purpose and pentest only.
  • The author will not be responsible for any damage ..!
  • The author of this tool is not responsible for any misuse of the information.
  • You will not misuse the information to gain unauthorized access.
  • This information shall only be used to expand knowledge and not for causing malicious or damaging attacks.
  • Performing any hacks without written permission is illegal..!

ShodanEye's screenshots:

ShodanEye Installation
   If you're using GNU/Linux, open your terminal and enter these commands:

   If you're a Windows user, follow these steps to install ShodanEye:
  • Download and run Python 3.7.x setup file from Python.org. On Install Python 3.7, enable Add Python 3.7 to PATH.
  • Download shodan-eye-master.zip file.>
  • Then unzip it.
  • Open CMD or PowerShell window at the Osueta folder you have just unzipped and enter these commands:
    pip install shodan
    python shodan-eye.py

Video Shodan Eye on YouTube:

Contact to the author:


More articles

About Me

My photo
Mightier than the sword, my pen is.